Paul Moore
Passwords: Using 3 Random Words Is A Really Bad Idea!
In 2015, the UK government released an article advocating the use of 3 random words in passwords, citing "pragmatism and algorithmic strength against common issues like brute force attacks". #Thinkrandom when creating passwords – #use3randomwords to make them https://t.co/6BlS8EqK7v pic.twitter.com/qtA43ffLf6 — Cyber Aware (@cyberawaregov) April 21, 2017 2 years later and a plethora of respected Twitter users continue to push this advice. If you're one of them (looking at you @WMPDigitalPCS
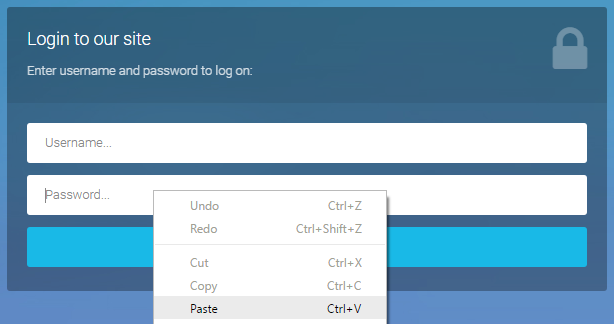
Don't let them paste passwords...
After months of tweets, emails & articles from eminent figures like Troy Hunt & the NCSC, it's about time I weighed in on the debate surrounding sites which disable a user's ability to paste passwords. The general consensus amongst many experts, including those mentioned above, is that disabling paste on password fields reduces security; the NCSC went one step further, calling it "completely pointless" and "damaging". So without further ado, allow me to explain why I believe disabling pas