Paul Moore
PwnPhone: Default passwords allow covert surveillance.
A few weeks ago, I was asked to observe an installation of several wireless access points & VoIP phones, with a view to making recommendations on how best to improve security while maintaining ease of deployment. It didn't take long for several trends to appear; chief amongst which was the use of We'll just use defaults, for now. That password will do, for now. Of course, as soon as the device burst into life, it's on to the next one. At which point, "now" becomes a distant memory, alo
Identity theft & payment fraud? That's ASDA price.
Back in March 2014, I contacted ASDA to report several security vulnerabilities and despite a fix promised "in the next few weeks", little appears to have changed. @Stuho1mez All of our sites are secure, I would advise using Chrome. Thanks, Beth — Asda Service Team (@AsdaServiceTeam) January 14, 2016 After 677 days and several tweets along a similar vein, my patience has finally run out. What's the problem? Two of the simplest and most prevalent exploits allow an attacker to quickly &
Privacy & Password Managers: A Reality Check
Before we begin, let me preface this by saying... I actually quite like Steve Gibson. For all his faults, he often raises very salient points on a variety of topics, typically surrounding security products & services. During the latest "Security Now / TWiT" episode on 20/10/2015, Steve & Leo Laporte featured a piece of 1Password news regarding Dale Myer's "1Password leaks your data" article. It's a little over 10 minutes long... It's no secret that Steve's a huge fan of LastPass and fo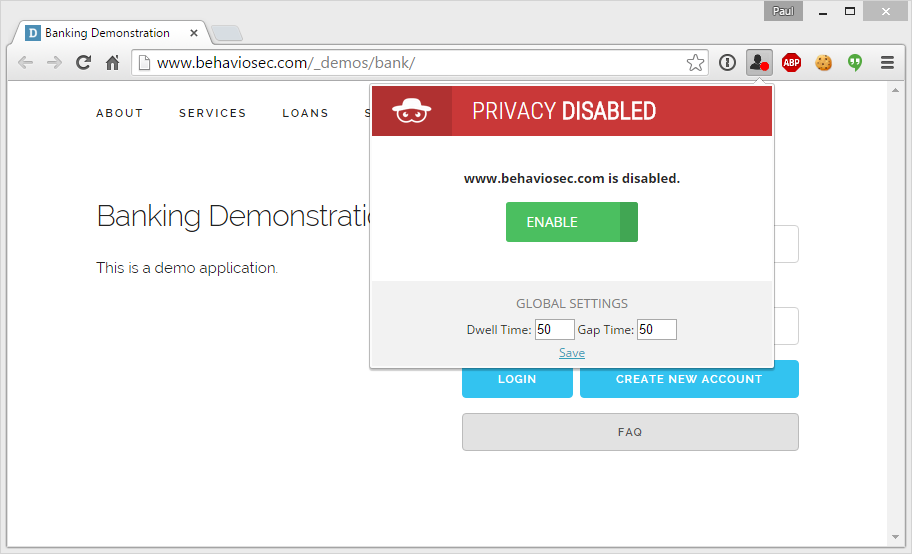
Behavioral Profiling: The password you can't change.
We're all familiar with the 3 basic categories of authentication. 1. Knowledge factors (passwords, PINs) 2. Possession factors (a software/hardware token - Yubikey/Google Authenticator/SecureID) 3. Inherence factors (fingerprint, heartbeat, iris/retina scanning) While the vast majority of sites use knowledge factors, a growing number are turning to multi-factor solutions in an effort to bolster security; to the detriment of the user experience. Cue continuous authentication / behavioral
Phishing attacks are evolving. The Vivian Gabb story...
"We have detect some unauthorized active on your account. Please update your detail as soon as possible" We've all had them; the notorious and grammatically inept phishing emails designed to strip us of our hard-earned money. The vast majority are destined for immediate deletion, but a growing number of sophisticated attacks are starting to emerge. Nobody understands this better than Vivian Gabb, a tennis coach from London who recently lost nearly £50,000 to fraudsters. Before you cast
Everykey: 3 years and $250,000... is it vaporware?
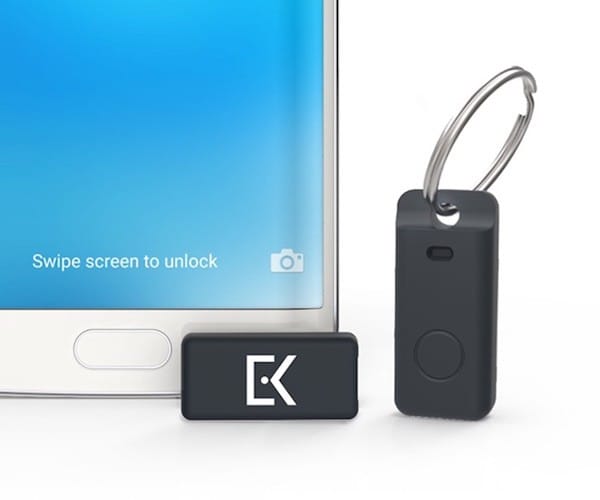
Update 22/12/2015 I've received several emails regarding this project over the last few months; another landing just a few moments ago. Unbelievably, Everykey has been delayed yet further... with delivery now estimated in February 2016. I'm very grateful to everyone for keeping me informed. However at this stage, there's not a great deal I can add to the discussions. It's a great idea with (I believe) real potential... but talk of "receiving samples" after 3 years and $1.2 million dollars
Boosting Your Galaxy Gear Battery Life
Just 22hrs after charging my Galaxy Gear, it's already minutes away from switching off and needing a recharge. I've read dozens of guides on how to extract as much life as possible from the tiny 312mAh battery, but few go into sufficient detail to help make informed decisions. So, here's a list (in order of effectiveness, highest to lowest) of steps you can take to increase your battery life. 1) Upgrade to Tizen Google's Android is great, but it was never designed for use on a smart w
SagePay: Breaching PCI Compliance... intentionally.
Update: 2:50PM 03/02/2015 Just minutes after this article went live, SagePay have once again removed the 56bit cipher. It is being actively monitored, so if it creeps back in, I'll update the article again. As one of the largest payment service providers in the world, SagePay has over 50,000 customers and processes over 4 billion payments each year. The website is festooned with security claims: Payment security and fraud prevention are two of our top priorities Thousands of
Roboform Security Revisited: Lies, Deception & Misnomers.
You may recall, I recently published an article entitled "How secure is Roboform: The 5 Minute Challenge". Well, 6 months have passed and although there's been no official public response from Siber Systems, they have made a number of comments to journalists and customers by email/Facebook and support tickets; during which I've been labelled as "misinformed", "unpleasant" and "sarcastic". There were no bugs in the first place. Roboform on Facebook Hmm. They edited the post.
Immobilise: Police Security Initiative Exposes 28 Million Records.
05/01/2015: Recipero, the company behind Immobilise, NMPR and CheckMEND have now mitigated this risk by limiting access to the "/verify" & pdf generation pages to only authorized users. You're no longer able to view records which you do not own, so although it's undoubtedly more secure, the inability to verify the authenticity of a certificate appears to render this process pointless. This exploit is known as a direct object reference, though I colloquially refer to it as the "open DOR" at